Security budgets have usually been argued line by line, with the CISO making the case for tools. That approach is failing. Boards now face AI adoption they did not plan, regulators who set reporting clocks measured in hours, and growing pressure to show that money goes where the risk is. This article sets out how to judge a security funding request on those terms.
- Fund against risk appetite, not last year’s spend. The Cyber Governance Code of Practice asks boards to define cyber risk appetite and check that resources match the agreed risks.
- Regulatory clocks now set the minimum. PRA-regulated banks and building societies will report qualifying operational incidents. The PRA expects the initial report within 24 hours of deciding the threshold is met, from 18 March 2027.
- AI is a new call on the budget, and controls lag. 31% of businesses use, adopt or consider AI. Only 24% of those have practices to manage AI risk.
- Accountability has to be named. The PRA expects the Chief Operations SMF24 to hold overall responsibility for incident reporting. Every control needs an owner.
- Cyber still loses the budget argument. 34% of businesses without cyber insurance said it was not a budgetary priority.
UK businesses with a breach or attack in the last 12 months
DSIT, Cyber Security Breaches Survey 2025/2026large businesses that reported a breach or attack
DSIT, Cyber Security Breaches Survey 2025/2026businesses with a board member holding explicit cyber responsibility
DSIT, Cyber Security Breaches Survey 2025/2026of AI-using businesses with practices to manage AI risk
DSIT, Cyber Security Breaches Survey 2025/2026Why the security budget is now a board decision
Breaches are now normal for larger firms.
Share of businesses reporting a breach or attack in the last 12 months, by size.
Source: DSIT, Cyber Security Breaches Survey 2025/2026.
Senior attention is high. Named board ownership is not.
Share of businesses, by size and measure.
Source: DSIT, Cyber Security Breaches Survey 2025/2026.
Cyber is still treated as a discretionary spend.
The survey’s stated reason for not holding cyber insurance, and the gap it exposes.
Source: DSIT, Cyber Security Breaches Survey 2025/2026. Our view: the gap between board attention and budget treatment is where funding cases fail.
The regulatory clock is already running.
Dates that shape the funding calendar.
Sources: DSIT; Bank of England; PRA rulebook.
Where a board’s funding case should sit on the TrustOps Maturity Model.
Level 3 funds controls. Level 5 funds outcomes against agreed tolerances.
Budget set by the last incident
Tools bought, owners unclear
Risk appetite agreed for the board
Quarterly reporting against tolerances
Spend moves with measured risk
What the board is really funding
A security funding request is a claim about risk. It says which losses the firm will accept, which it will not, and what it costs to change the odds. A board that approves budgets without that link is paying for activity it cannot defend to a regulator, an auditor or its own members.
Our view: the question has moved from “what does security cost?” to “which risk does this reduce, to what tolerance, and who answers for it?”
Why the old funding model breaks
- It is tool-led. Requests start from a product and justify it afterwards, so the board cannot see which risk each line reduces.
- It runs on an annual cycle. Regulatory reporting now runs on clocks measured in hours and days.
- AI spend sits outside it. Teams adopt AI tools through departmental budgets, so the security budget never sees the exposure.
Regulation has moved from guidance to clocks
Five obligations shape the funding case. Only some are final, so each needs a different planning assumption.
| Obligation | Status at 12 October 2026 | What it means for funding |
|---|---|---|
| PRA PS7/26, operational incident and third-party reporting | Final rules. Applies from 18 March 2027 | Initial incident report within 24 hours of deciding the threshold is met. Final report within 30 working days of resolution. Annual register of material third-party arrangements |
| PRA SS1/23, model risk management | Current version effective 23 April 2026 | For firms with internal model approval. AI is in scope where it is a model. Validation capacity needs funding |
| Cyber Security and Resilience Bill | In the House of Lords. No Royal Assent yet | Scenario plan now. Do not budget as settled law |
| EU AI Act, high-risk obligations | Regulation (EU) 2026/1744 in force since 27 July 2026. Annex III high-risk obligations apply from 2 December 2027, Annex I from 2 August 2028 | Build the AI system inventory now, ahead of the 2 December 2027 deadline |
| Cyber Governance Code of Practice | Published 8 April 2025. Voluntary, but a benchmark boards are measured against | Risk appetite, resource assurance and quarterly reporting with tolerances |
Status checked against the primary publications on 12 October 2026. Confirm before relying on any date.
How AI changes the request
AI adds spend in three places: securing staff use of AI tools, securing models and data pipelines the firm builds or buys, and defending against attacks that use AI. The mistake is to fund all three as one general “AI” line. Each should sit against the system it protects, with a named owner.
The DSIT survey shows the gap. Of the 31% of businesses using, adopting or considering AI, only 24% had cyber practices or processes to manage AI risk. That is the gap a funding case should close.
Four questions for your next board or ExCo
Require formal reporting on at least a quarterly basis, set suitable metrics to track, and agree tolerances for each.
Cyber Governance Code of Practice, Principle E, Action 2, DSIT, April 2025Where funding cases go wrong
01Funding the tool, not the outcome
A product is bought, then justified by its features. Nobody can say which risk fell, or by how much.
02Treating AI as a separate budget
A general AI line hides exposure in the systems that carry it, and the owners of those systems are not asked.
03Using insurance to close the gap
Insurance transfers part of the financial cost. It does not reduce the likelihood of an incident or the duty to report one.
04Reporting activity instead of tolerance
Counts of alerts and patches tell the board that work is happening. They do not show whether risk is within tolerance.
A funding sequence that holds up
Our view: sequence the spend so the board sets the risk appetite before the money moves, and regulatory obligations are funded before discretionary projects.
Fund the baseline first, then the AI controls, then measure
Indicative timescales. They depend on your governance cycle, systems and change capacity.
Where do you stand?
Use the maturity model in the stage above to place your board. Level 3 is where the case becomes defensible: risk appetite agreed, owners named, and regulatory obligations funded before discretionary work.
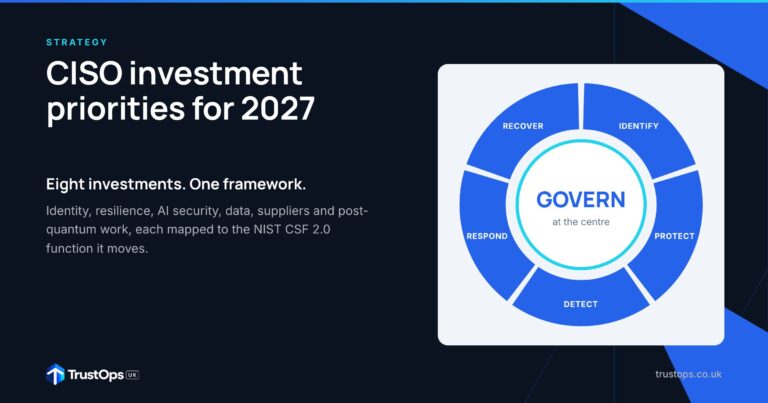
For the line-by-line allocation across NIST CSF 2.0 functions, read What CISOs should invest in for 2027, mapped to NIST CSF 2.0.
For a shorter set of questions to open the conversation with your board, read 5 questions your board should ask about cyber risk.
Take the free 15-minute assessment to see where your funding case sits, or book a scoping call to work through the regulatory calendar with us.
Sources (6 primary sources)
- DSIT, Cyber Security Breaches Survey 2025/2026 (30 Apr 2026)
- DSIT, Cyber Governance Code of Practice (8 Apr 2025)
- Bank of England, PS7/26, Operational incident and third-party reporting (18 Mar 2026)
- Bank of England, SS1/23, Model risk management principles for banks
- UK Parliament, Cyber Security and Resilience Bill (status checked 12 Oct 2026)
- EUR-Lex, Regulation (EU) 2026/1744, Digital Omnibus on AI, recital 40 (adopted 8 Jul 2026, in force 27 Jul 2026)
Dated 12 October 2026. Regulatory status is checked on that date and may change. This article is general information, not legal or financial advice. Views marked “our view” are TrustOps UK’s own.
Follow TrustOps UK: trustops.co.uk · X @TrustOpsUK · Instagram @trustops.co.uk · hi@trustops.co.uk